Check Point Technology Partner · AI Security Australia
AI Security Company in Australia: Use AI Safely, Without the Data Leaks
Your team is already using ChatGPT, Copilot, Claude and Gemini, often through personal accounts. We discover every AI tool in use, stop sensitive data leaking through prompts and lock it all down on Australian-hosted infrastructure.
Your free assessment report includes:
- AI apps in use, ranked by risk
- Data exposure examples, with users and apps identified
- AI policies tailored to your teams
- A clear per-user quote for ongoing protection
Powered by Check Point Workforce AI Security · Hosted on Australian cloud servers · Live in under 15 minutes
AI apps and platforms detected and governed
To deploy, with zero downtime
Free assessment with a full risk report
Data hosted on Australian cloud servers
The AI Risk Problem
Generative AI Speeds Up Your Business. It Also Puts Your Data at Risk.
AI tools save your people hours every week. They also open a new, mostly invisible path for client records, financial figures, passwords and source code to leave your business. Most of it happens in browser tabs and personal accounts that firewalls and traditional security tools were never built to see.
Enterprise AI Shadow Usage & Data Exposure Velocity
of workers use AI in the workplace
of workplaces have an official AI policy
of workforces operate without an AI security policy
of enterprise GenAI access happens through personal accounts
of unauthorised data movement from corporate environments now runs through GenAI tools
of data has been transferred to AI and machine learning applications
The five AI security gaps we see most often
- Shadow AI: staff use AI apps nobody approved, creating blind spots you can't monitor or audit.
- Data exposure in prompts: a quick "summarise this contract" can send client names, pricing or health details to a third-party model.
- Outdated controls: legacy DLP and DNS-based filters read keywords, not conversations, so risky intent in a prompt slips straight through.
- Governance gaps: IT can block a whole website, but can't set rules for what one person shares with one AI tool.
- Unchecked AI agents: desktop agents, coding assistants and MCP connections can act on files, systems and credentials with little oversight.
Can you answer these six questions today?
- 1Which AI apps, approved or not, are being used across your business?
- 2Who is using generative AI, and what for?
- 3What sensitive data is being shared in prompts and file uploads?
- 4How is employee AI use governed and enforced?
- 5Are your AI tools secure and compliant with your obligations?
- 6How do your AI agents score on a risk assessment?
Context-Aware Prompt Protection
AI Security That Understands Context, Not Just Keywords
Keyword-based tools either block too much or miss what matters. Our AI-powered DLP reads the intent behind a prompt, so it can tell a confidential business disclosure from an everyday personal question, even when both use the same words.
Select an example below to see how our contextual engine analyzes intent in real time:
Key element evaluated: acquire
Flagged and held: confidential M&A information. The user is asked to remove the details or justify the business need.
Confidential M&A and financial disclosure detected.
Three-Layer Protection Model
Our AI Security Services: Discover, Govern, Protect
We set up, run and report on AI security in three layers, so you can say yes to AI without losing control of your data.
Discover every AI tool in use
See across every AI tool, agent and action in your business, sanctioned or shadow, with insight into user intent, data flows and agent behaviour.
Capabilities & Controls Enforced:
- Detect and monitor 16,000+ AI apps, including shadow AI and MCP servers
- Break down AI activity by app, session and user: what was asked, what data went in, and where it came from
- Find AI features running inside your connected SaaS platforms, in one dashboard
- Track adoption trends and see which apps drive the most risk
- Search a full AI app catalogue, including apps nobody in your business uses yet
Infrastructure & Sovereignty
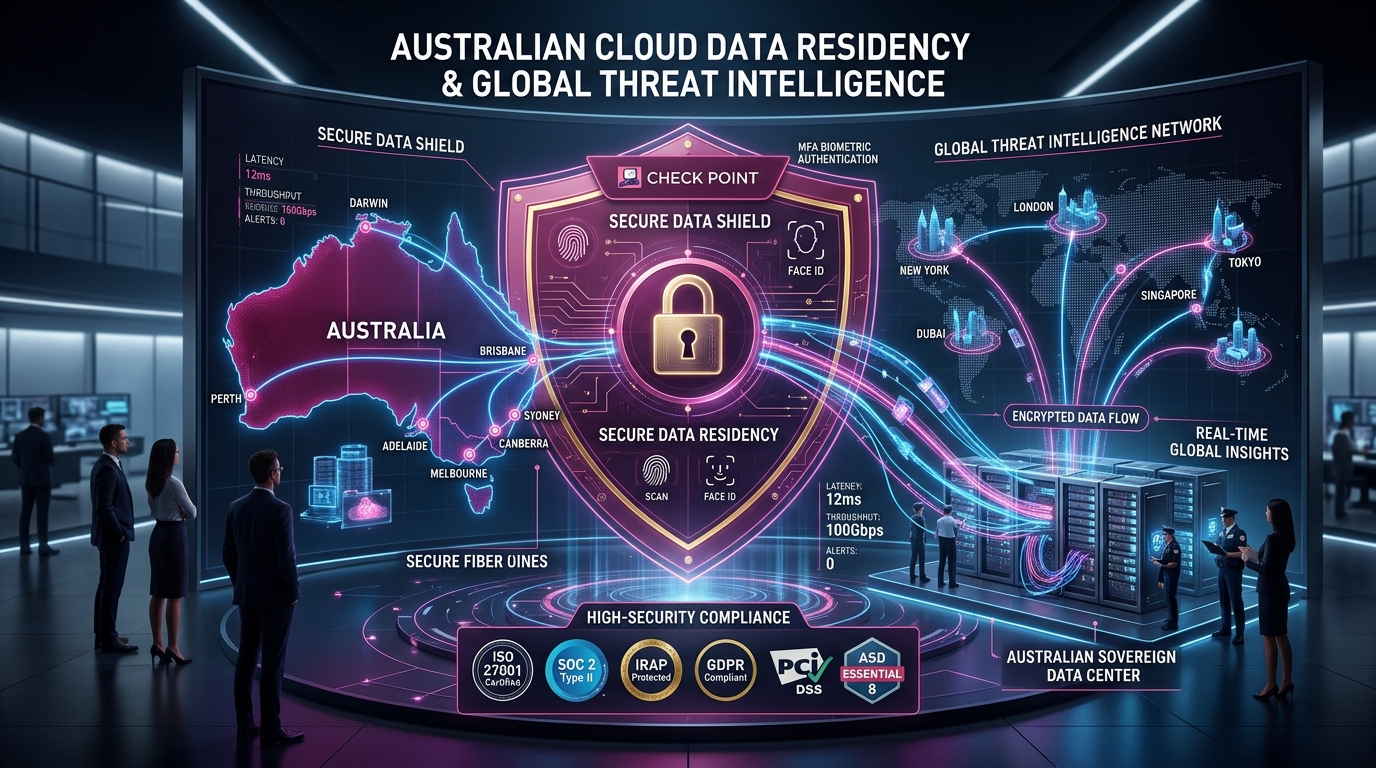
Secure Identity, Controlled Access, Australian Data Residency
Prompt protection only works when the right people are signing in, each person has the right level of access, and your data stays where your obligations say it should. Every deployment includes all three.
Multifactor Authentication (MFA)
A stolen password should never be enough. We enforce MFA on every admin and user account that touches your AI security platform, and extend it to your approved AI apps through your identity provider, such as Microsoft Entra ID or Google Workspace.
- MFA on all admin and console access
- MFA for company AI accounts, including ChatGPT, Copilot, Claude and Gemini
- Alerts on suspicious sign-ins to AI tools
Access Control
Not everyone needs the same AI access. We set role-based access so each team gets the AI tools and data permissions its work requires, and nothing more.
- Role-based access per team, such as finance, HR, developers and front office
- Personal AI accounts restricted or blocked; approved company accounts kept open
- Least-privilege permissions for AI agents and their connections to files, systems and SaaS
- Every policy change and access event logged for audit
Australia-Based Cloud Server Deployment
Your AI security platform, activity logs and reports are deployed on Australian cloud servers. Your data stays onshore.
- Supports your Privacy Act 1988 and Australian Privacy Principles obligations
- Meets data residency expectations from healthcare, legal, financial and government clients
- Faster performance for Australian users, with local support from our Melbourne team
MFA and restricted privileges are core controls in the ACSC Essential Eight, the baseline mitigation strategies for Australian organisations.
Essential Eight BaselineComprehensive Attack Surface Protection
Full Coverage, Everywhere Your People Use AI
AI isn't one website anymore. It lives in browsers, desktop apps, SaaS platforms and autonomous agents. Our AI security covers every one of them.
ChatGPT, Claude, Gemini, Perplexity, DeepSeek and thousands more
Copilot in Microsoft 365, AI features in Google Workspace and other connected apps
AI writing and summarising extensions that read what's on screen

Check Point Workforce AI Security
Discover · Govern · Protect
Backed by ThreatCloud AI
Agents that can open files, run commands and act on your behalf
Coding assistants such as GitHub Copilot, Cursor and Claude Code, including API keys in code
Model Context Protocol servers that link AI agents to your systems and data
AI threats we help you stop
- Sensitive data leakage: PII, financials, health records, credentials and source code shared in prompts or uploads
- Shadow AI: unapproved apps and personal accounts outside your control
- Prompt injection and jailbreaks: hidden instructions that make AI tools ignore their rules
- Rogue agent actions: AI agents deleting, sending or changing data they shouldn't touch
- Insecure MCP and SaaS connections: AI tools linked to corporate resources without oversight
- Credential exposure: API keys and passwords pasted into chatbots and coding assistants
- Compliance breaches: personal information processed by AI in ways your policies don't allow
Full AI Lifecycle Governance
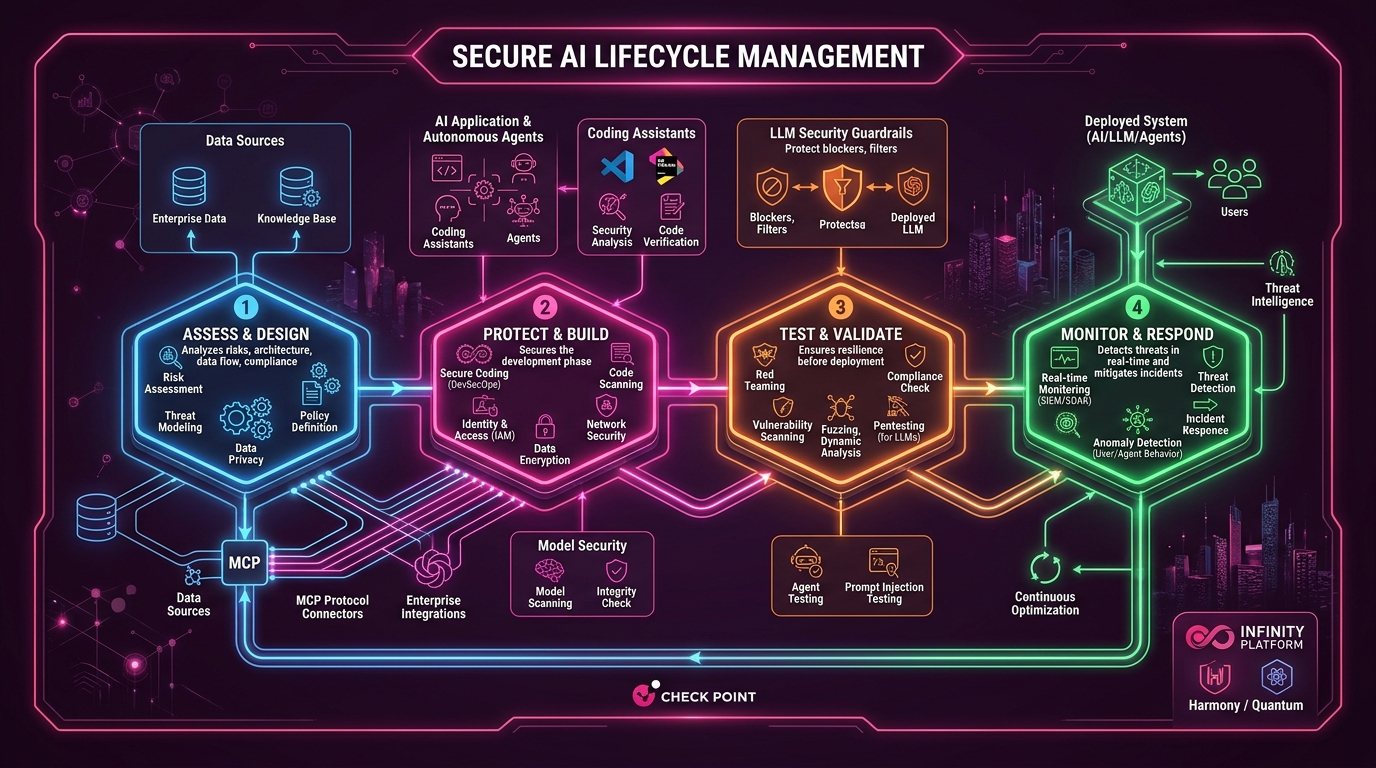
Secure the AI Systems Your Business Runs, Across Their Whole Lifecycle
If your business runs a customer chatbot, an internal AI assistant or an AI agent connected to your systems, it needs more than a usage policy. We secure it at every stage, from design to day-to-day operation.
Assess
Map every AI system you run, the data it touches and who can reach it. Identify risks against recognised AI security frameworks.
Protect
Apply least-privilege access, MFA and data masking. Keep sensitive data out of prompts, training data and knowledge bases.
Test
Test chatbots, agents and RAG systems against prompt injection, jailbreaks, data leakage and unsafe tool use, guided by the OWASP Top 10 for LLM Applications.
Monitor and respond
Watch for abnormal prompts, data leakage and risky agent behaviour in production, with an AI-specific incident response plan ready if something goes wrong.
Platform Capabilities
Everything Included in Our AI Security Service
| Feature | What it does for you |
|---|---|
| Shadow AI discovery | Finds every AI app staff use across 16,000+ platforms, approved or not |
| Work vs personal account detection | Tells company AI accounts apart from personal ones and applies different rules to each |
| Contextual AI data loss prevention | Reads the meaning of a prompt, so confidential data is caught even without obvious keywords |
| Real-time redaction | Replaces credentials, PII and financial data with labelled placeholders before a prompt is sent |
| File and image protection | OCR scans uploaded files and screenshots for sensitive data |
| Use-case classification | Shows what AI is used for across your business, from marketing to legal to coding |
| Granular policies | Allow, ask, detect, redact, prevent or block, per app, user, team and data type |
| Action validation wizard | Users see a clear warning and can justify a business need, so work isn't blocked unnecessarily |
| AI agent and MCP protection | Monitors desktop agents, coding assistants and MCP servers, and blocks risky actions |
| SaaS integration governance | Controls AI features and third-party integrations inside your SaaS platforms |
| Multifactor authentication | MFA on every admin and user account connected to your AI tools |
| Role-based access control | The right AI access for each team, with least privilege for AI agents |
| Australian cloud hosting | Platform, logs and reports stay on Australian servers |
| Audit trails and compliance reports | Custom reports for the Privacy Act, Essential Eight, GDPR, HIPAA and the EU AI Act |
| Threat intelligence | Backed by Check Point ThreatCloud AI: 90+ security engines, 50+ of them AI-powered, synced globally in under 2 seconds |
| Fast, zero-downtime deployment | Rolls out across browsers and devices in minutes, with no complex setup |
Zero Downtime Evaluation
See What Your Business Is Missing in 14 Days
Try it before you commit. A live demo takes under 5 minutes, setup takes under 15, and the assessment runs in discovery mode first, so there's zero disruption to your team.
Kick-off and setup (30 minutes)
We complete the initial setup, configure MFA and admin access, define your use cases and policies, and run the first scan in discovery-only mode.
First results review (1 hour)
We set up automated reporting and walk you through the shadow AI found, data leakage events and sensitive information shared. Then we move from detect to prevent mode.
Prevention review (1 hour)
We analyse prevent mode in action, review the workflow, validate the end-user experience and apply best-practice policies.
Report and recommendations (1 hour)
You receive a full AI security report, personalised DLP policies and a clear plan, with pricing and no obligation to continue.
What you get at the end:
- A list of every AI app used in your business, ranked by risk
- Real examples of sensitive data shared with AI, with users and apps identified
- Ready-to-use AI policies tailored to your teams
- A clear, fixed per-user quote for ongoing protection
Compliance & Standards
AI Security Mapped to Australian and Global Standards
Clients, insurers, auditors and regulators increasingly ask how you control AI. We map your AI security controls, audit trails and reports to the frameworks that matter.
Privacy Act 1988 and Australian Privacy Principles
Stops personal information reaching AI tools and keeps logs onshore.
Privacy Act and AI for small businessACSC Essential Eight
MFA, restricted admin privileges and application control applied to AI tools
Australia's Voluntary AI Safety Standard
Supports its guardrails on accountability, risk management, data governance and testing
ISO/IEC 42001
Evidence for an AI management system: AI inventory, policies and audit trails
NIST AI Risk Management Framework
Supports its Govern, Map, Measure and Manage functions
OWASP Top 10 for LLM Applications
Testing baseline for chatbots, AI agents and RAG systems
GDPR, HIPAA and the EU AI Act
Customisable reports for businesses with overseas clients or operations
One Control Set, Every Framework
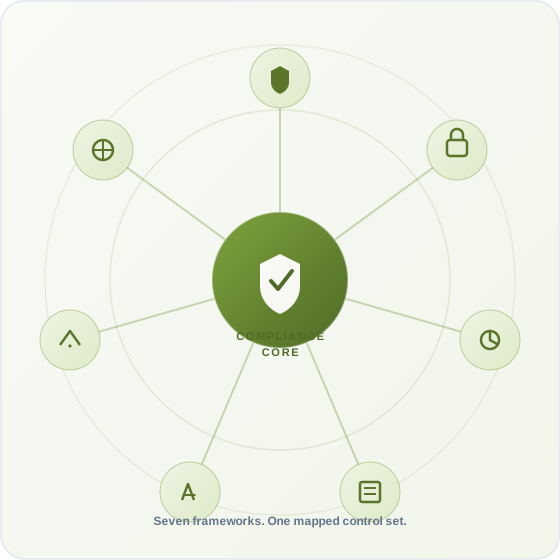
We help you meet these standards. Formal certification is issued by an accredited body.
Business Impact
What Secure AI Adoption Means for Your Business
Outcome Strength by Area
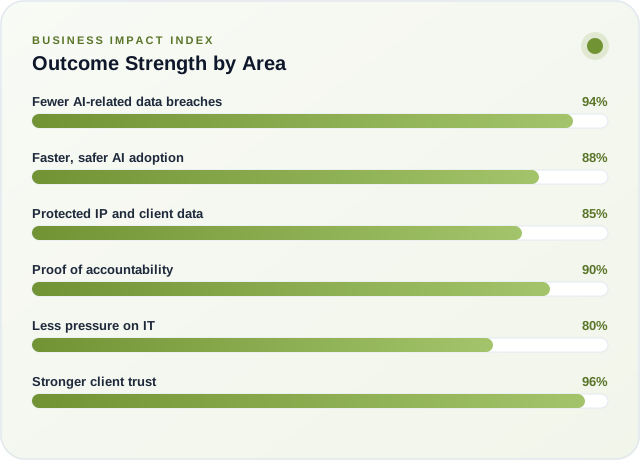
Fewer AI-related data breaches
Sensitive data is caught and redacted before it leaves your business
Faster, safer AI adoption
Staff keep the AI tools they rely on, inside clear guardrails
Protected IP and client data
Contracts, pricing, source code and client records stay out of public models
Proof of accountability
Audit trails and reports show clients, insurers and auditors exactly how AI is controlled
Less pressure on IT
We run discovery, policy tuning, monitoring and reporting for you
Stronger client trust
You can answer "how do you use AI with our data?" with confidence
Industry Specialisation
AI Security for Australian Industries Handling Sensitive Data
Healthcare and clinics
Patient notes and Medicare details pasted into chatbots to write referrals or summaries
Legal firms
Client names, contracts and case details shared with AI for drafting and review
Finance and accounting
Client financials, TFNs and bank details used in AI-generated reports
Real estate and property
Tenant and vendor personal information in AI-written listings and emails
Construction and engineering
Tender pricing and commercial terms uploaded to AI to speed up bids
Software and IT teams
API keys and credentials exposed through coding assistants and AI agents
Government suppliers and NFPs
Citizen or member data processed by unapproved AI tools
The Zynex Advantage
Why Choose Zynex as Your AI Security Company in Australia
Enterprise-grade AI security technology.
We deploy Check Point Workforce AI Security, built on Check Point's acquisition of AI security leader Lakera and backed by ThreatCloud AI intelligence that prevents billions of attacks every year.
More than a firewall rule.
We don't just block AI sites. We read the content of prompts and stop sensitive data from leaving, while approved AI keeps working.
Security that doesn't slow your team down.
Staff get clear guidance and a chance to justify a business need, not a wall of blocked pages.
Australian-hosted, Australian-supported.
Platform and logs on Australian cloud servers, a Melbourne-based team, and reporting aligned to the Privacy Act and Essential Eight.
Identity and access built in.
MFA and role-based access control come standard with every deployment, not as add-ons.
Fully managed for you.
We handle setup, policy tuning, monitoring and monthly reporting, so you don't need an in-house AI security team.
Low-risk start.
A live demo in 5 minutes, setup in 15, and a free 14-day assessment with no lock-in.
Common Questions
AI Security FAQs
Official Check Point Technology Partner · Melbourne Support
Find Out What Your Team Is Sharing With AI
Book a free 30-minute call with our AI security team. We'll run a live demo in under 5 minutes, show you what a 14-day assessment would uncover in your business, and give you a straight answer on risk, timing and cost.
No obligation · Free 14-day assessment · Australian-hosted · MFA and access control included